Every automated action,
a rite.
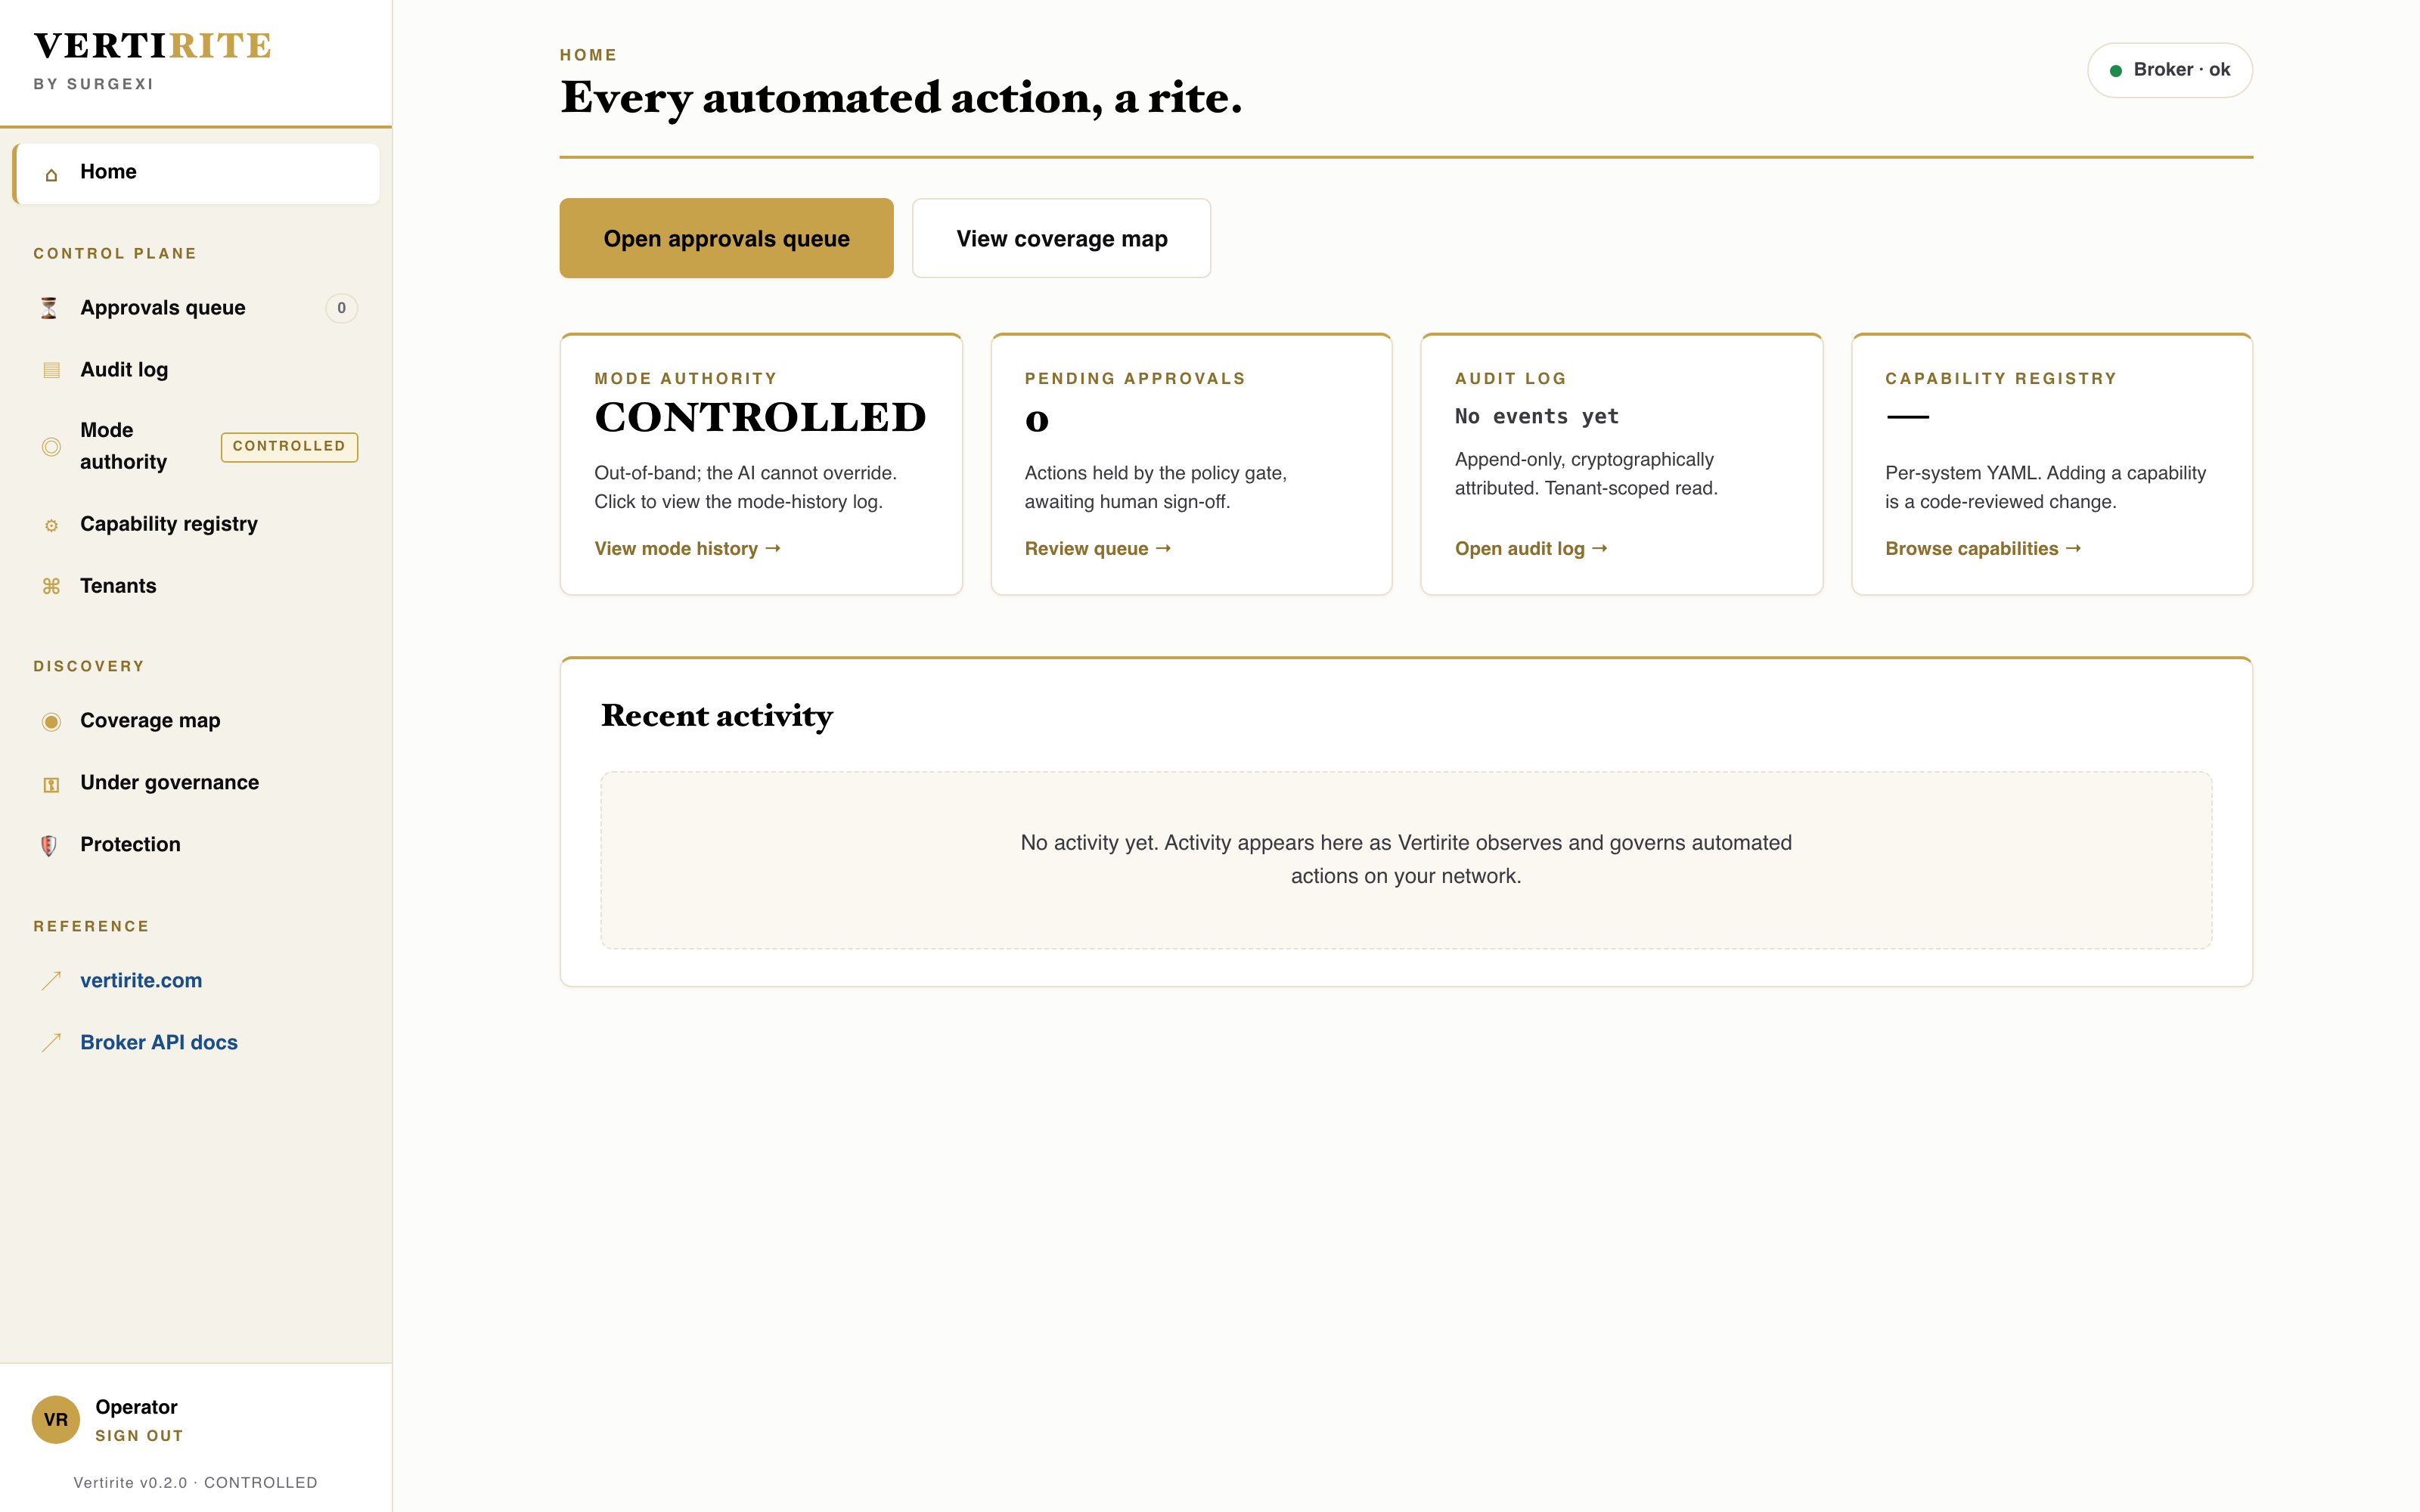
Vertirite finds every AI and automation already touching your systems, ranks what they can reach, and puts a human gate in front of the actions that can hurt you — before they run. Every action authenticated, every gated decision on the record. You keep the keys.
The control plane isn’t itself an AI. There’s no model in it — nothing to jailbreak, nothing to hallucinate, nothing new to govern. It runs air-gapped.
The Demo is by approved request: hosted, read-only, sample data, 7 days. Watch the gate work; nothing connected on your side.
AI agents · RPA bots · cron jobs · CI/CD · service accounts · webhooks. Works with any AI, any framework. No vendor lock-in.
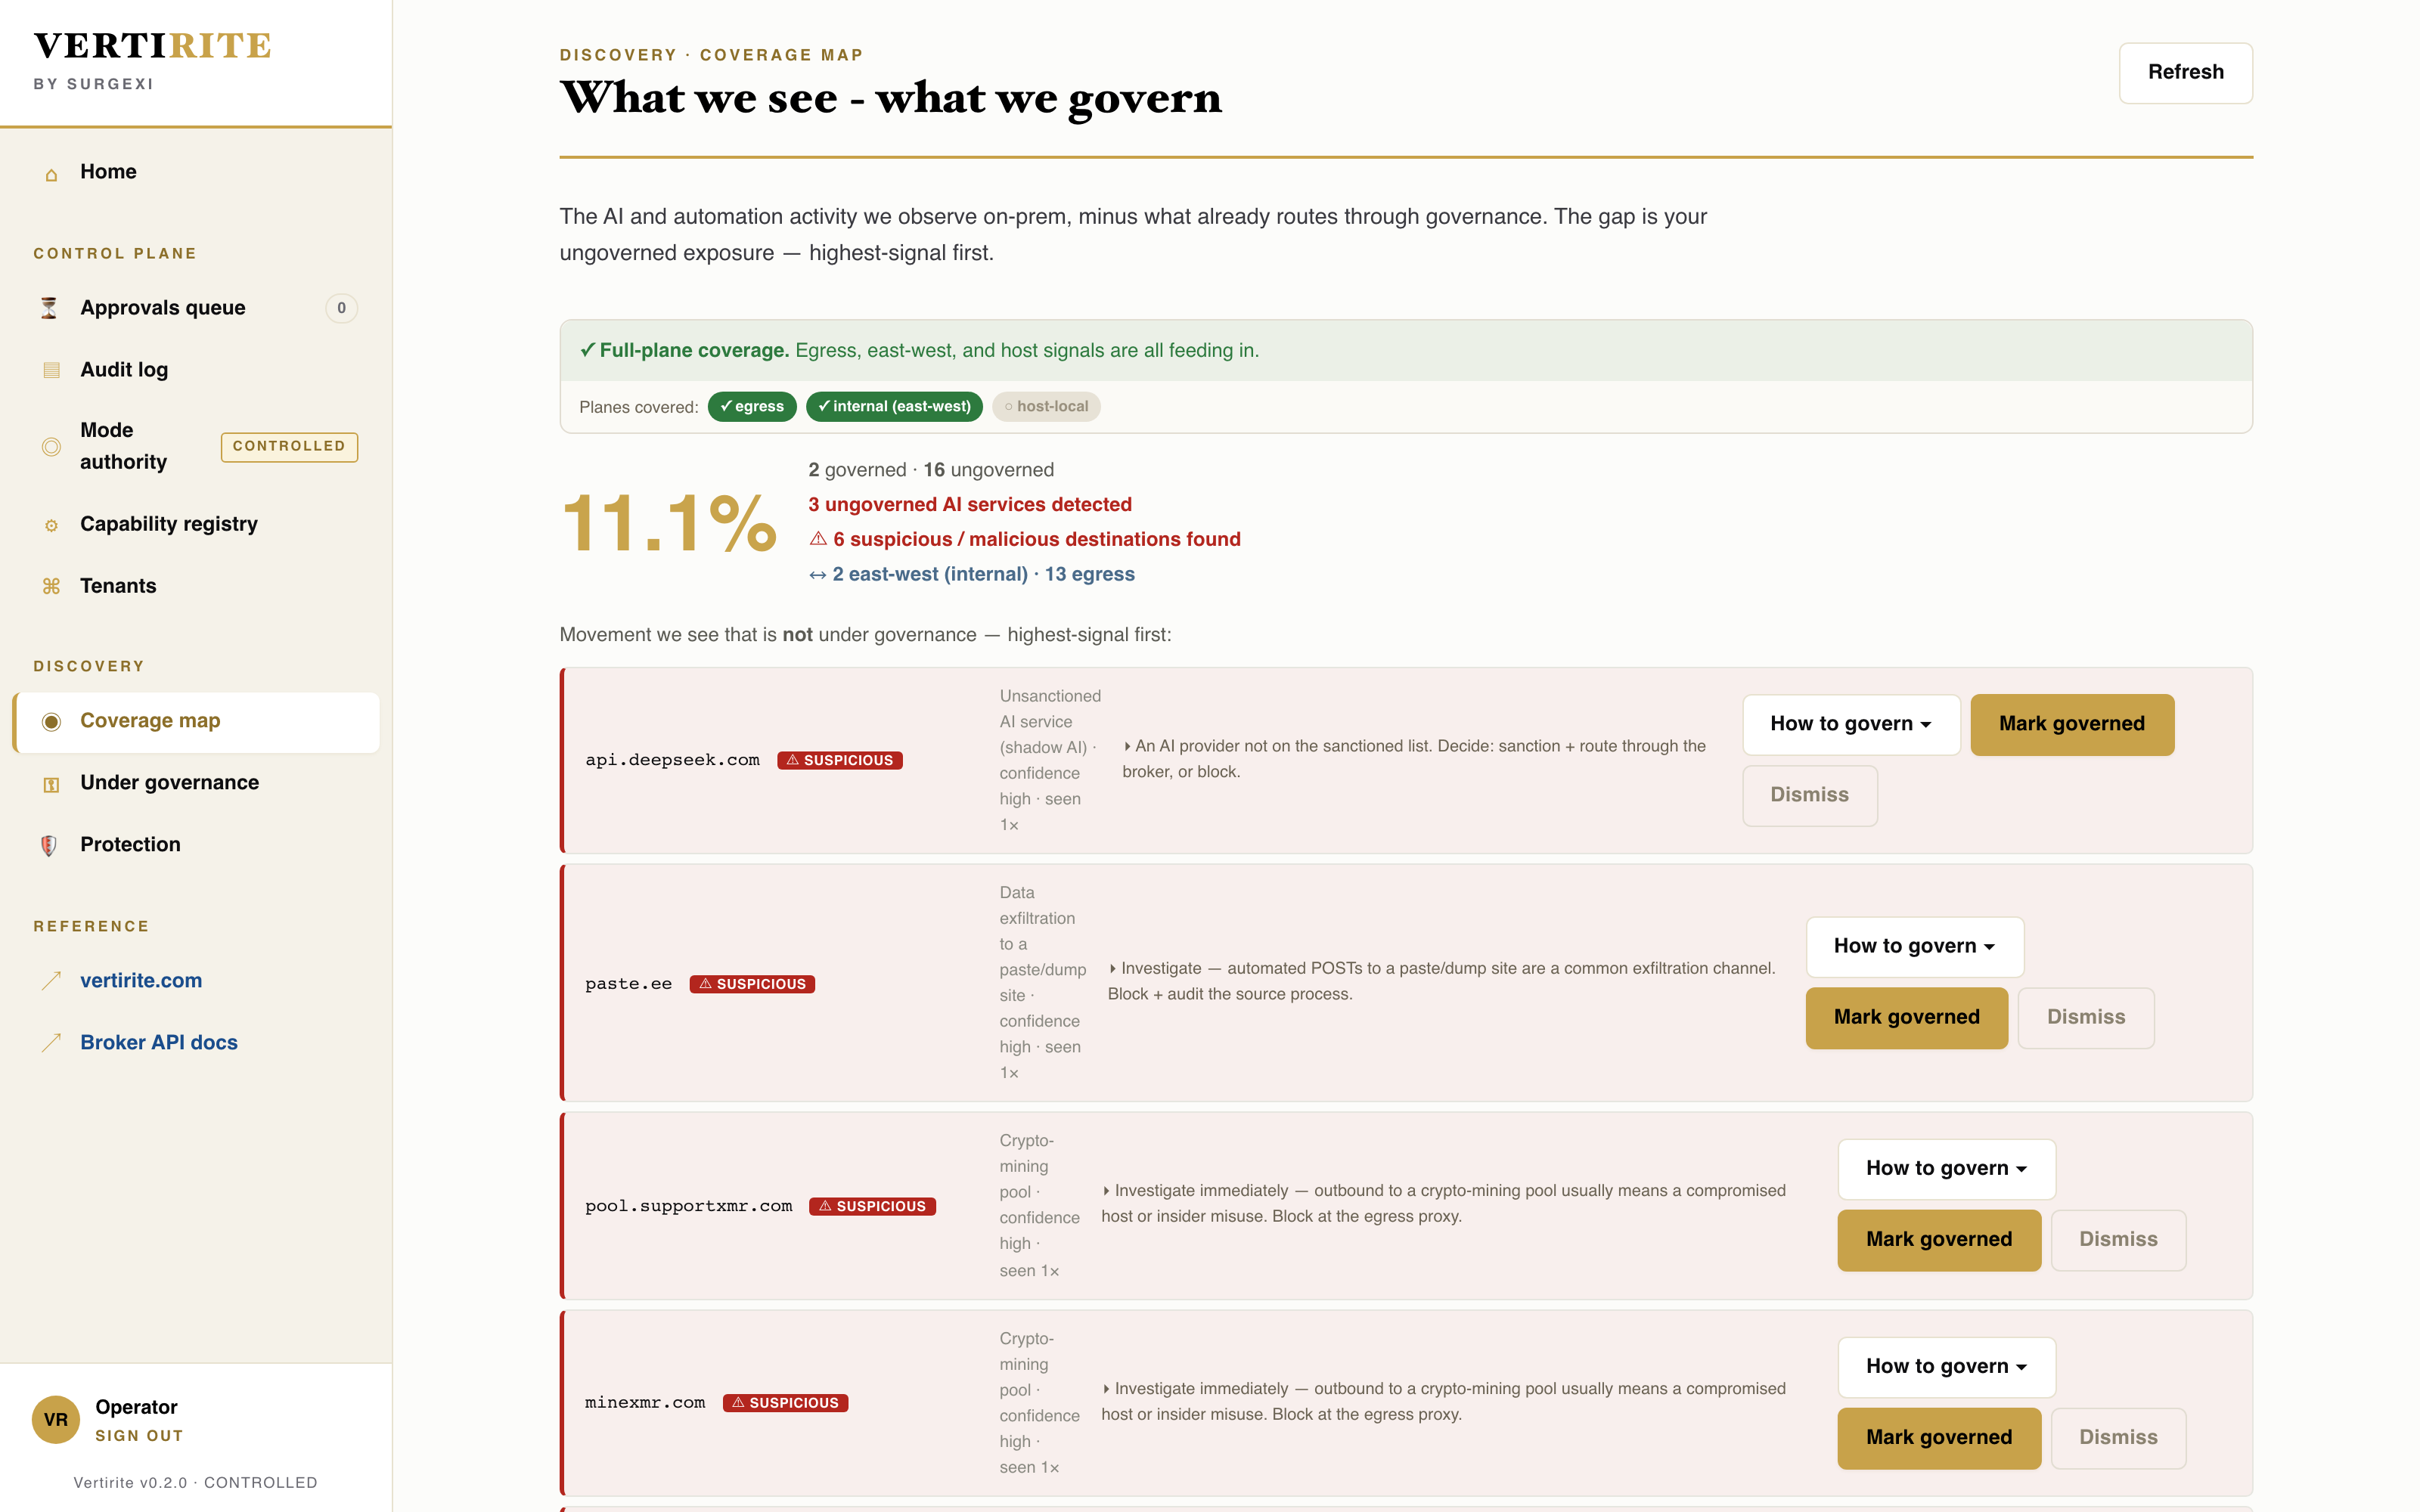
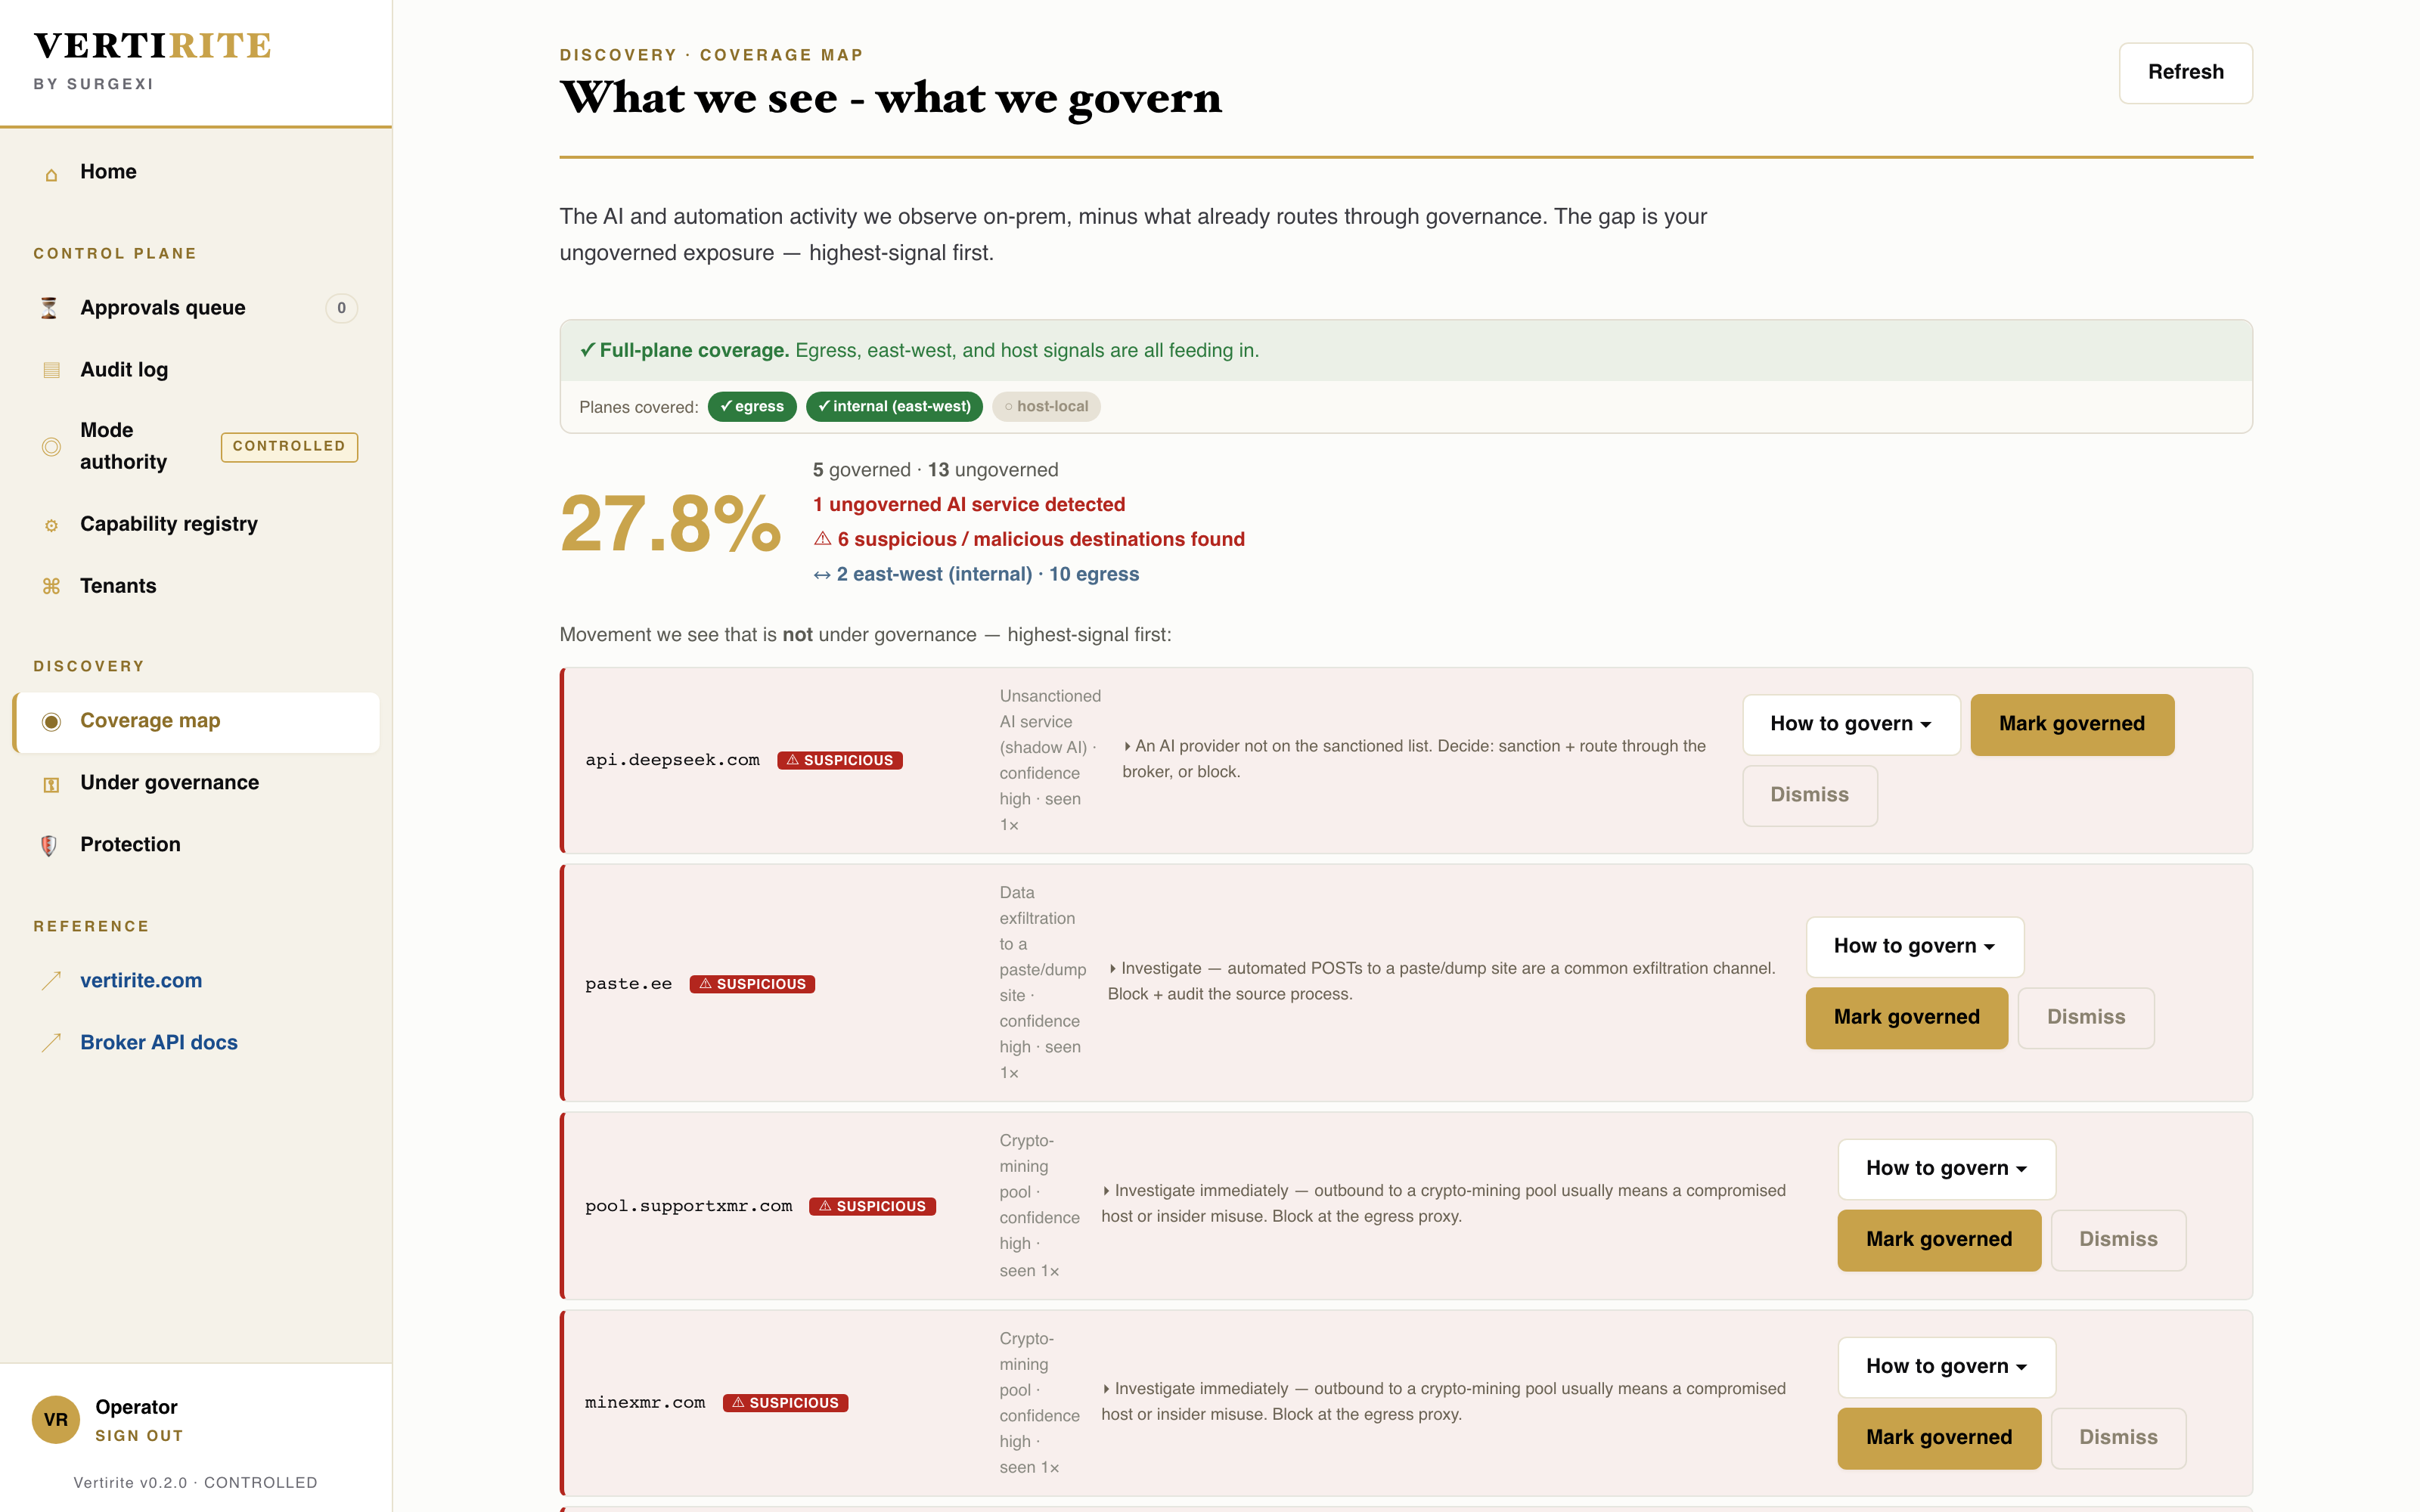
The console, live. Shadow AI, crypto-mining, and data-exfil destinations flagged and ranked — each one click from being brought under governance.
Built first for
The problem, in one breath
“Every department wants AI. The board is asking. But legal won’t let me wire ChatGPT into our customer database, and they’re right — I can’t tell them what the AI is doing, can’t roll back its actions, can’t put a stop button on it during an incident.”
— the dilemma Vertirite is built to solve
Step one — discovery
What we see, minus what we govern, is your exposure.
You can’t point us at the AI to govern — that’s exactly why you called. So Vertirite finds it: every model call, automation, and service account crossing your perimeter or moving east-west inside it, matched against a live threat catalog and ranked highest-signal-first.
- ›Sanctioned AI — routed through the broker, audited.
- ›Shadow AI — surfaced the moment it appears.
- ›Crypto-mining & data-exfil — flagged, one click to block.
Step two — six gates every automated actor passes.
Not the wire — the brain. Vertirite governs the resources an AI can’t fabricate: credentials, money, and network egress.
Policy gate
Out-of-band mode authority — AUTONOMOUS / CONTROLLED / ESCALATION / LOCKDOWN. No automated caller can override it.
Capability registry
Per-system YAML defining exactly which roles can call which endpoints. Adding a capability is a code-reviewed change.
Mutual TLS + signed JWT
Every action authenticated end-to-end. A compromised client cert is not the ability to forge role claims.
Approval queue
Human-in-the-loop review for any flagged action. Web UI, CLI, or webhook — your team's choice.
Containment chokepoints
Egress, credential, and irreversible-action gates. The stop button that actually stops it, mid-incident.
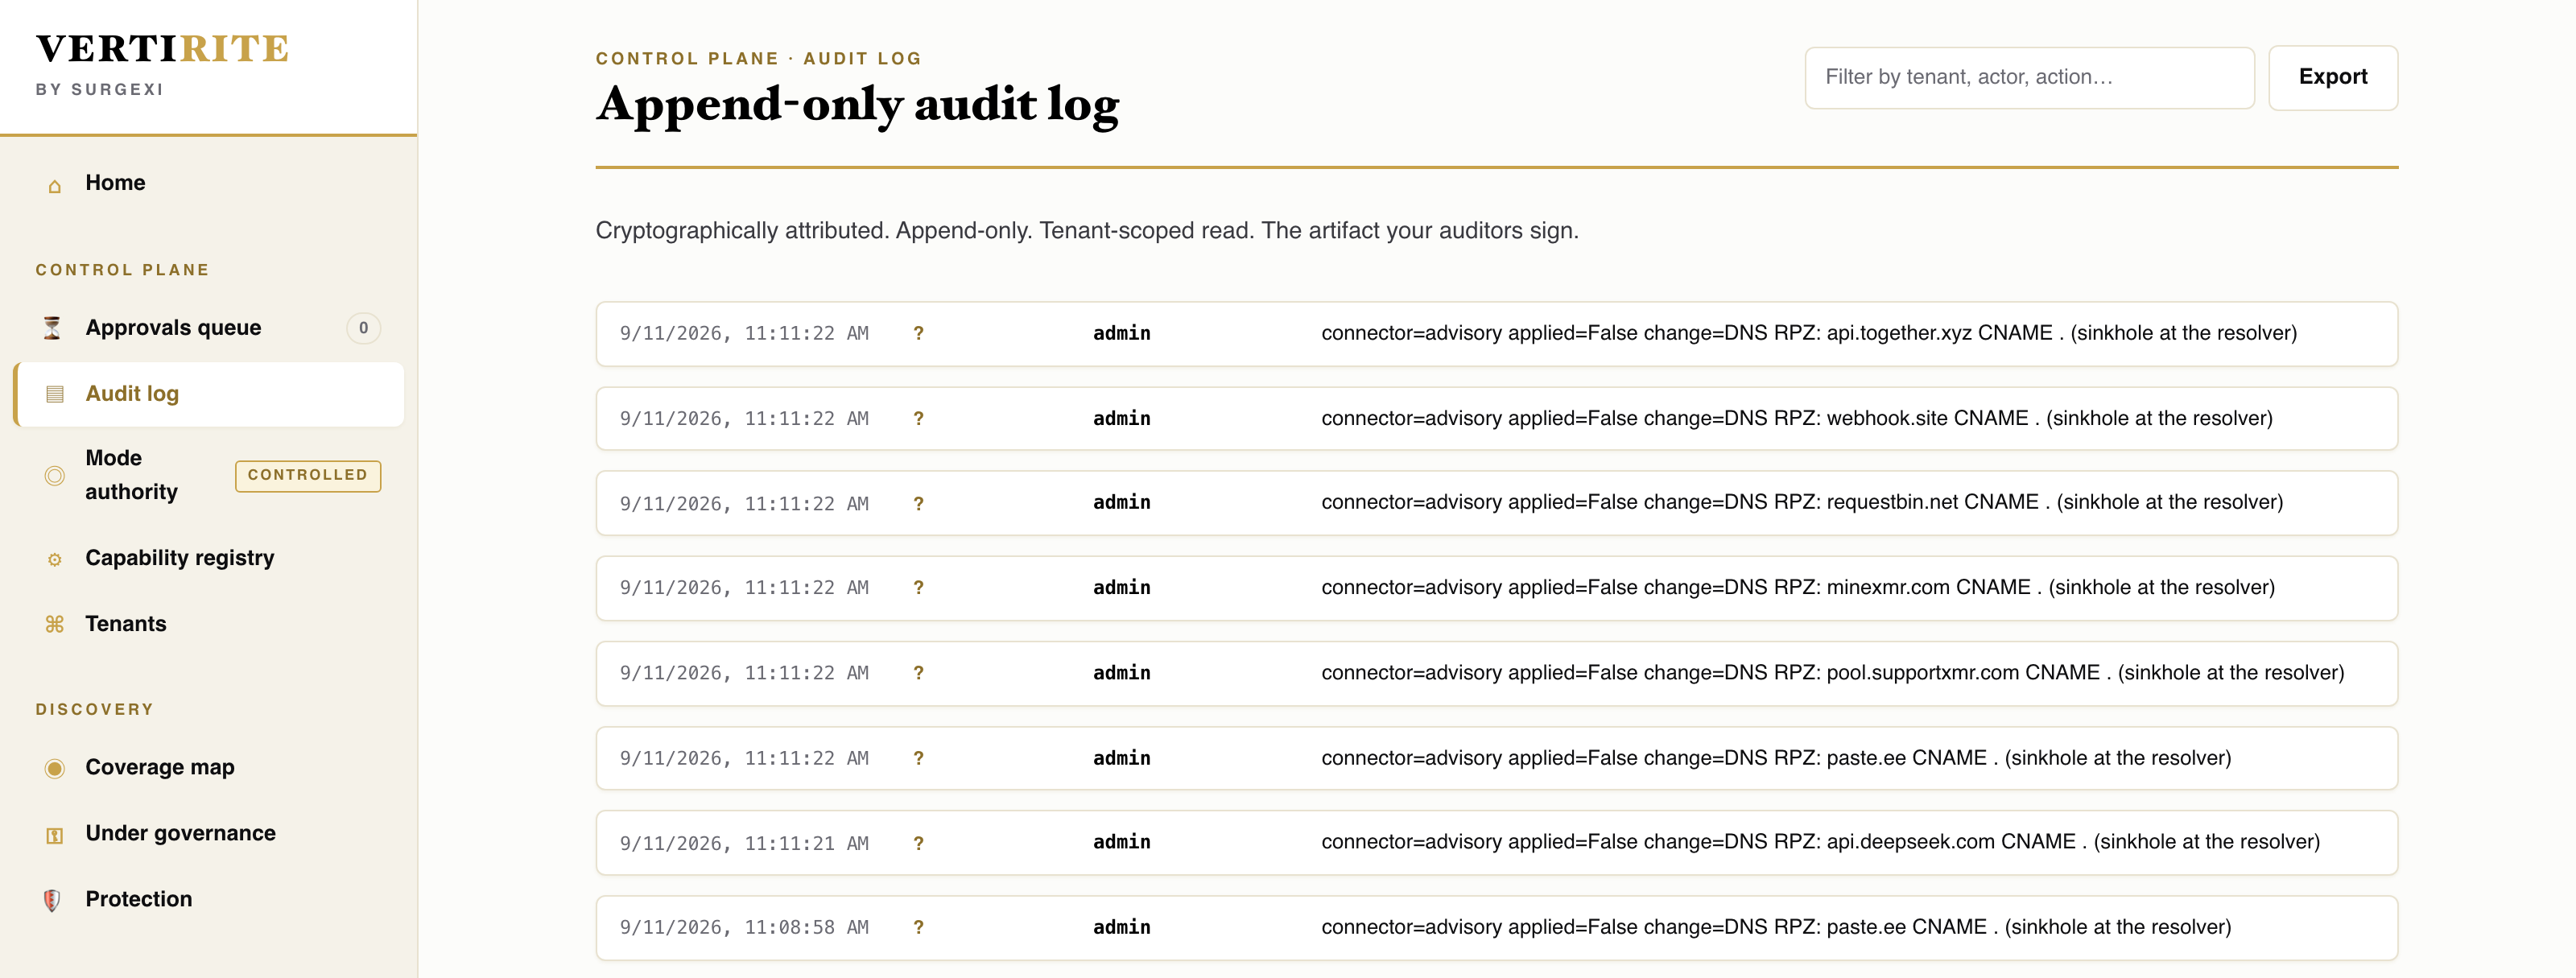
Audit log
Every approval decision is recorded: who asked, who decided, what, when, and under which mode. SOC2 and HIPAA-aligned by design. Signed, tamper-evident export coming.
See it in action
Discover. Govern. Prove it.
The Demo — by approved request
Don’t take our word for it. Watch the gate work.
The Demo is hosted, read-only and runs on sample data for 7 days. You see the console, sample discovery results, and a sample approval queue and audit trail: approved, denied, timed out. It can’t gate anything, and nothing of yours is connected.
Vertirite Theatre
See it run against live scenarios — nothing installed.
Theatre replays real day-in-the-life scenarios — medical, accounting, industrial — through the actual broker code against an isolated database, in real time. We run it on a 30-minute screenshare (nothing installed, nothing connected on your side). Watch tickets triage, approvals queue, the audit log fill — then take home the resulting PDF.
Pilot pricing keeps procurement out of the way.
Vertirite runs on your hardware. Pilot and subscription customers can review the source under a confidentiality agreement. Three steps: a Demo (by approved request, hosted, read-only, sample data, 7 days), a Pilot ($5,000, 60 days, on your hardware, gating on, credited toward year one), then an annual Subscription.
See full pricing →Want to see it first? Request a demo →
How this was built — and by whom
The engineering behind the control plane.
Vertirite didn’t start as a pitch deck. It grew out of open engineering work on the two hard problems underneath it: how to give an AI tools without giving away control, and how to run it privately on your own hardware. That work is public — read the thinking, not a download.
secure-agent-patterns
The threat model and control-plane design behind Vertirite: treat model output as untrusted, route every side-effecting action through one choke point, deny what’s outside its grant, and hold high-risk actions for a human — with a runnable proof.
Read the patterns on GitHub →onprem-ai-infra
How we run AI privately on real hardware — topology, hardening baseline, monitoring, and failure runbooks. The air-gapped, data-stays-on-your-network posture Vertirite is designed to run in.
See the infrastructure on GitHub →More open engineering from the founder at github.com/tsmith-surgexi.